AI Agent Attacks
Operationalizing Enterprise MCP Governance Across Heterogeneous Agent Stacks
Enterprises must enforce unified identity and centralized policy before MCP servers proliferate.
Tobias Krenz
· 9 min read
Enterprises must enforce unified identity and centralized policy before MCP servers proliferate.
Slack agents need identity controls and traceable tool calls to stop unauthorized access.
Enterprises must detect MCP attacks hidden inside encrypted application traffic.
Enterprises need central governance to scale AI agents safely beyond MCP's connectivity layer.
Secure MCP deployments require six layers of controls beyond the protocol itself.
Unified control planes centralize MCP credentials and access policies across projects.
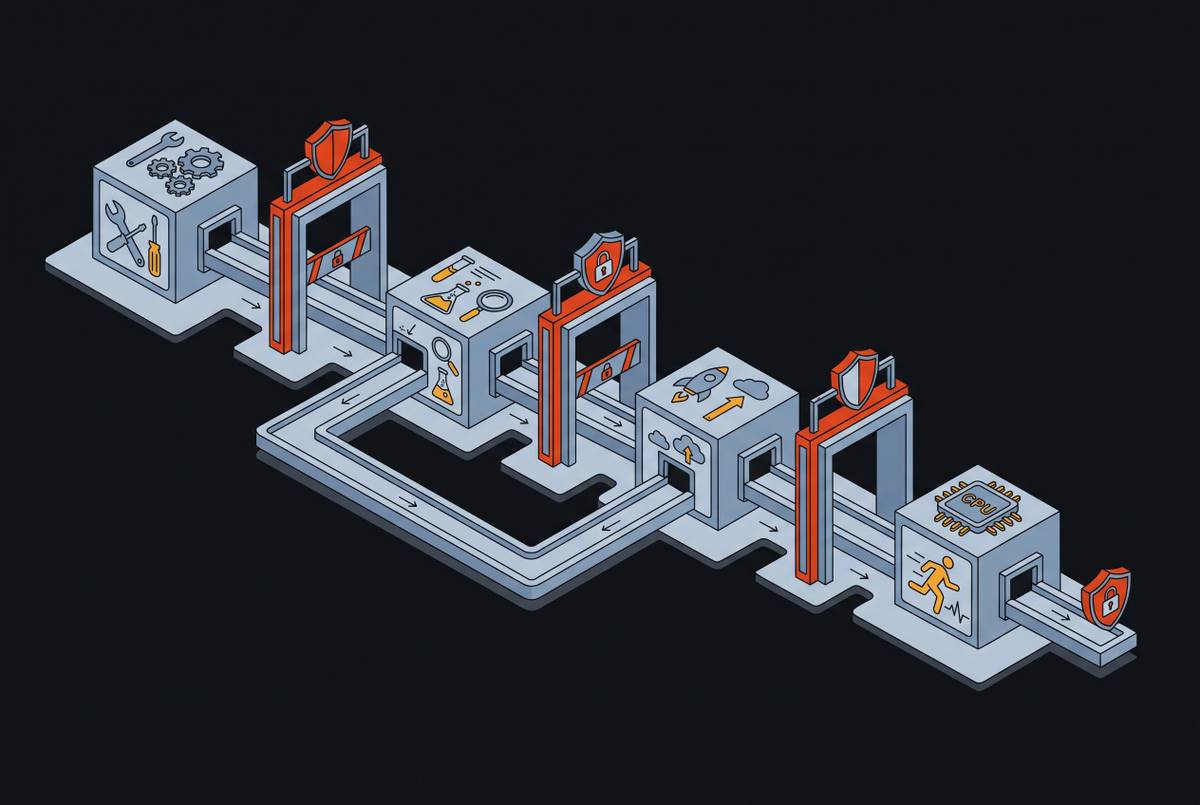
Security gates must span design through operations to defend agents' unpredictable execution paths.
Enterprises need portable identities and bounded delegation to secure agent connections safely.
ISO/IEC 42001 needs supplementary controls for agent tool calls and delegation chains.
Upgrading MCP requires auditing security controls at each protocol version change.
Build audit trails that prove authorization, scope, and action for every AI agent decision.
AARM provides runtime context checks that static OAuth cannot enforce for MCP tool calls.