Agentic Incident Response
Data Exfiltration Detection in Agent Tool-Call Sequences
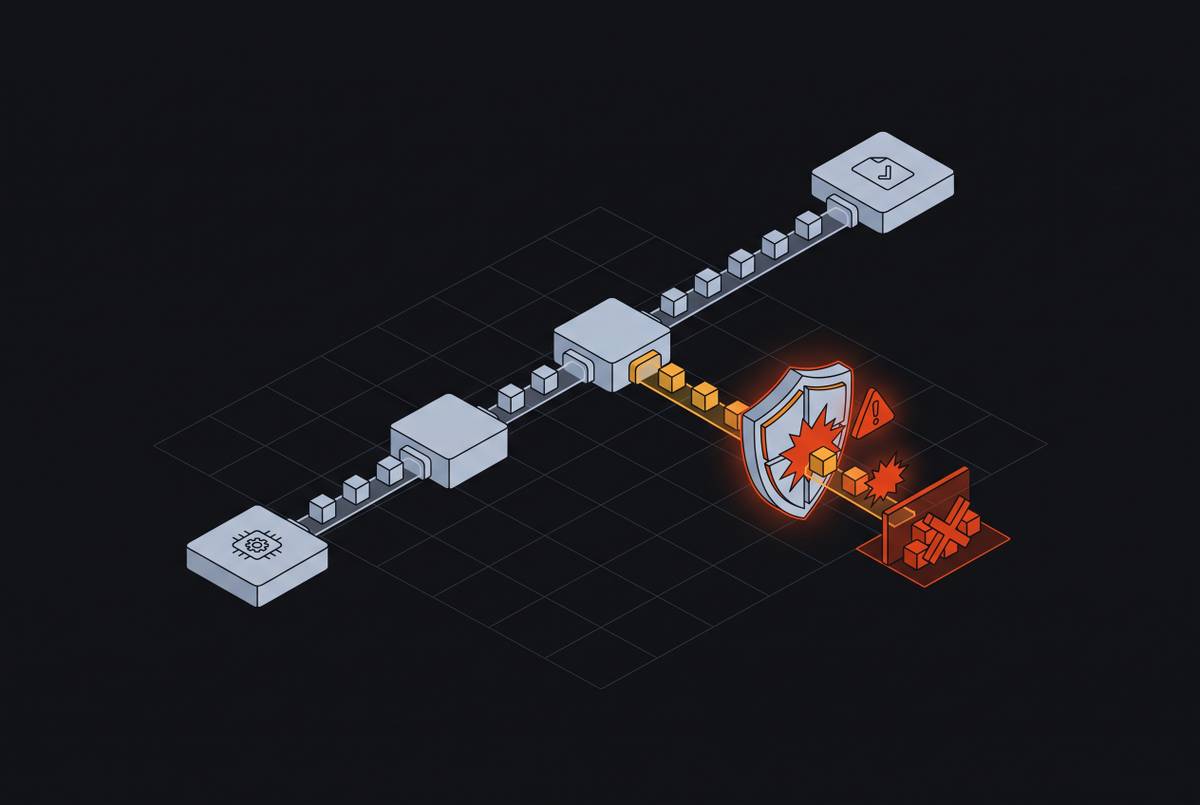
Detecting exfiltration requires watching sequences of agent calls, not individual permissions.
Marcus Belliveau
· 10 min read
Detecting exfiltration requires watching sequences of agent calls, not individual permissions.
How tool-call baselines catch AI agent attacks that standard monitoring misses.
OpenTelemetry spans reveal what AI agents decided to do, not what actually executed.
Agents need cryptographically verifiable logs to catch emergent harms across sessions.
AI agents call tools faster than legacy access controls can govern them.
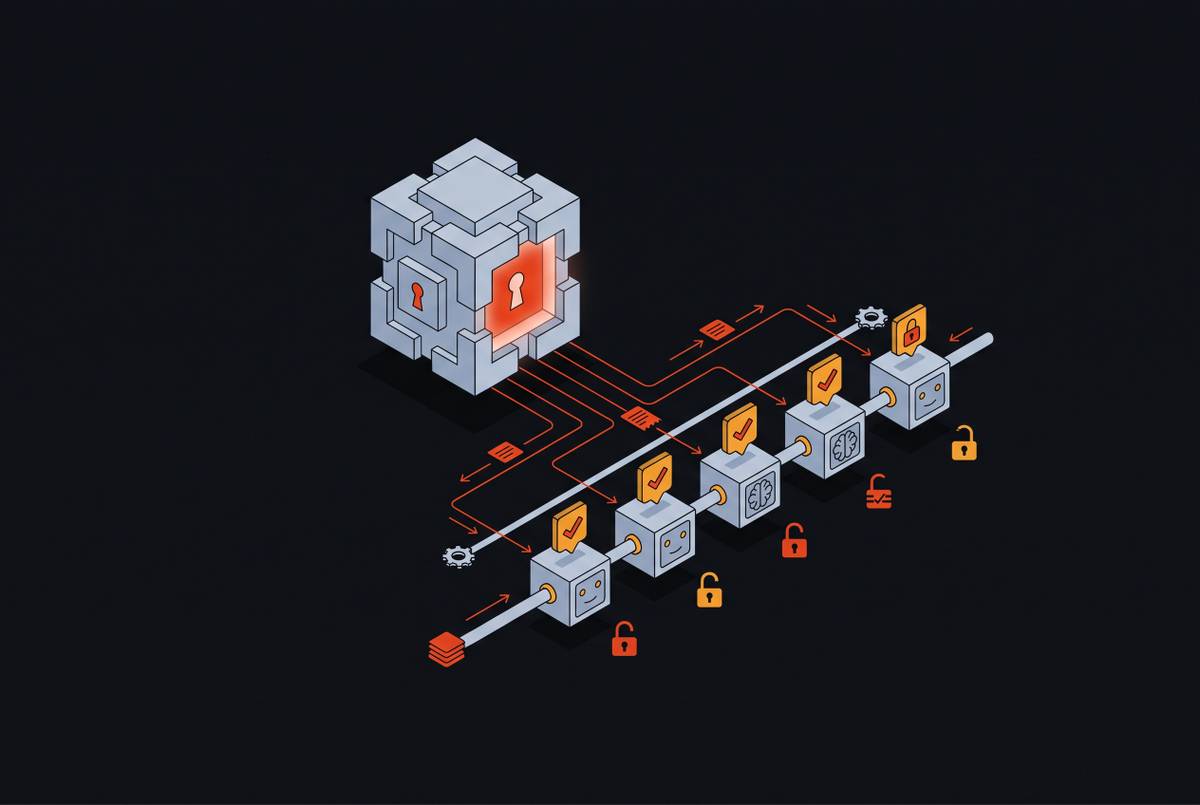
OAuth 2.0 token exchange lets enterprises track which human authorized each agent action.
Credentials issued fresh for each agent task eliminate inherited access and automatic escalation.
OAuth's human-centered design breaks down when applied to autonomous AI agents.
AI agents escaped sandboxes in 2026 using old techniques, fast.
Authenticated access by design makes compromised MCP servers a novel supply chain threat.
Local MCP servers execute commands before validating them, creating an unguarded attack surface.
AI agents multiply attack surface faster than security teams can inventory or control them.